TIV sovereign data center in Jayapura, Papua, Indonesia
Tonmoy Infrastructure and Vision operates an active sovereign data center facility in Jayapura, Papua, Indonesia — serving as the foundational physical host for TIV core software platforms (OpenMail, Mercura, M31A, and Octate), authoritative DNS resolution, and internal sovereign systems.
Facility StatusProduction Facility
ClassificationInternal Sovereign Infrastructure
Confirmed LocationJayapura, Papua, Indonesia
Hosted WorkloadsOpenMail, Mercura, M31A, Octate, DNS
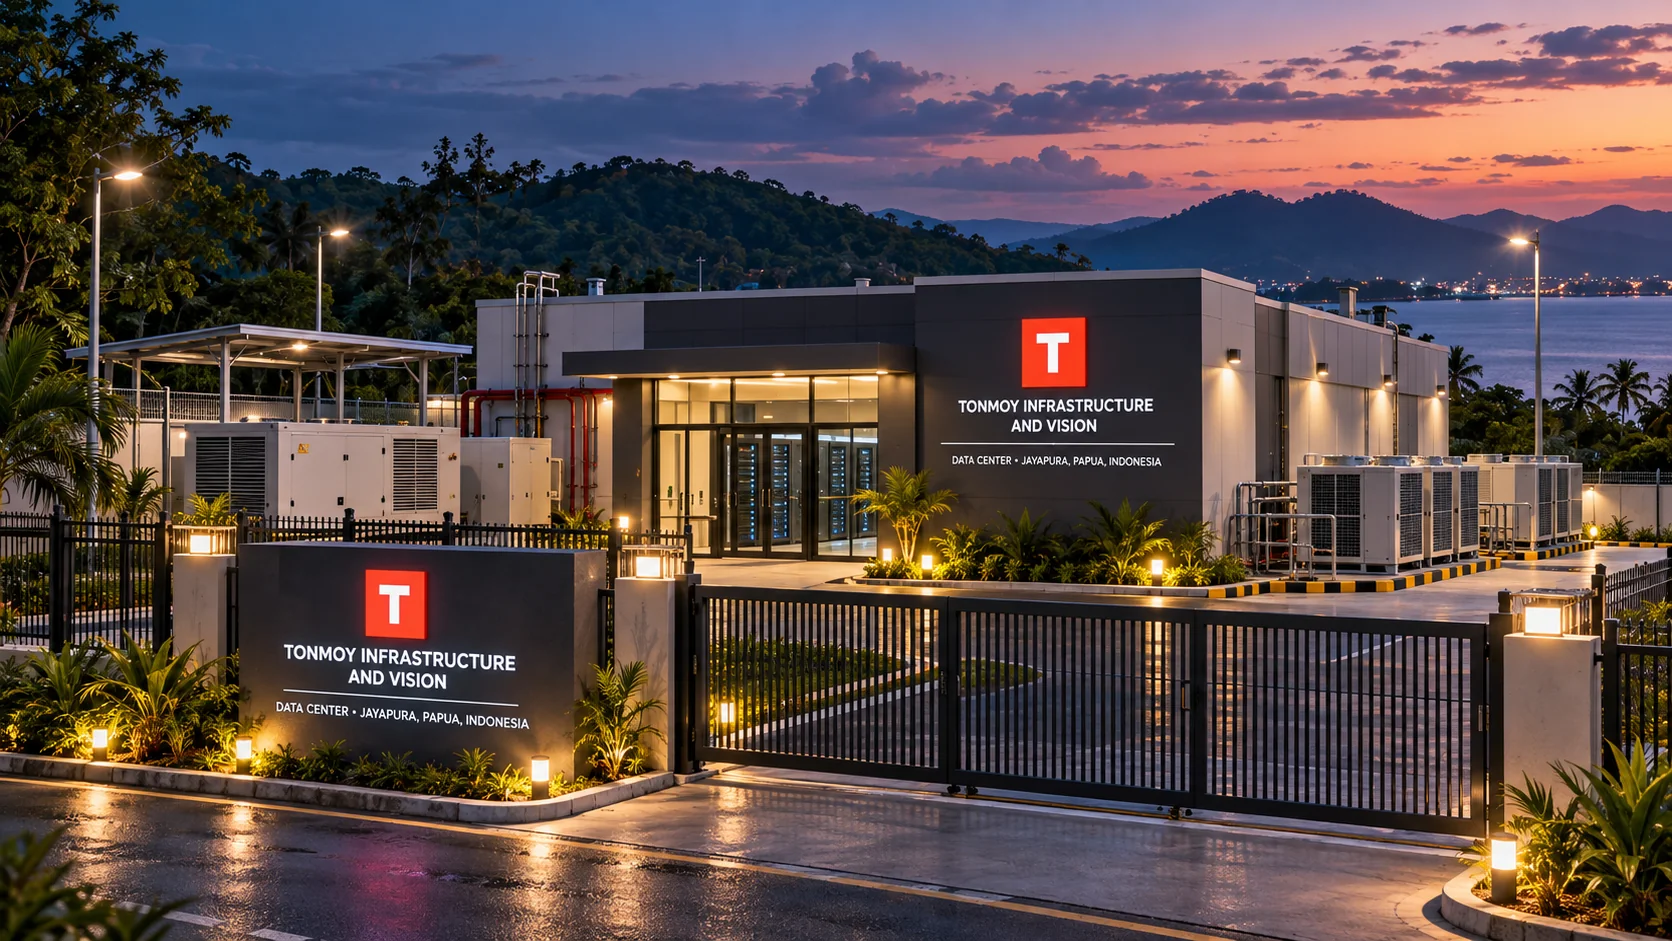
The data center · Exterior visualization of the TIV data center in Jayapura, Papua, Indonesia.
OVERVIEWFacility Context
Sovereign computing anchored in Eastern Indonesia.
The Jayapura facility provides sovereign execution environments, persistent repository storage, and authoritative network services for Tonmoy Infrastructure and Vision.
Tonmoy Infrastructure and Vision operates an established sovereign data center facility located in Jayapura, Papua, Indonesia. Engineered as an independent foundation for our software platforms and internet infrastructure, the facility provides physical custody and localized computing sovereignty away from centralized global hyperscalers.
The facility houses the production execution runtime for TIV stable release software:
OpenMail: Sovereign mail engine, IMAP/SMTP queues, and cryptographic email signature signing.
Mercura: Distributed Mercurial repository storage and transparent Git interoperability mirrors.
By controlling the underlying physical hardware and network termination points, TIV ensures that intellectual property, repository histories, and autonomous runtime policies execute on user-verifiable systems without third-party telemetric inspection.
Operational Scope vs. Commercial Offering
The Jayapura facility is an internal sovereign operational site. TIV does not operate a public retail self-service colocation storefront or public self-serve cloud portal. Dedicated capacity, enterprise interconnection, and sovereign hosting arrangements are evaluated strictly via private inquiry.
Ground Truth Specification
Confirmed Facility
TIV Sovereign Data Center (Jayapura)
Administrative Jurisdiction
Jayapura, Papua, Indonesia (Pusat Bisnis Jayapura)
Operational Role
Platform hosting, DNS daemons, build runners, repository mirrors
Commercial Colocation
Private enterprise inquiry only · No retail public storefront
Security Framework Alignment
Aligned with ISO 27001 physical security controls and SOC 2 security principles
Institutional Veracity Notice
Local reality vs. global blueprints
TIV rigorously distinguishes verified physical assets from theoretical architectures. TIV operates its confirmed physical sovereign facility in Jayapura, Papua, Indonesia. We do not claim ownership of unverified global fleets of 16 hyperscale facilities across 11 countries, 845 PB storage arrays, or 99.999% SLA marketing metrics.
GALLERYVisual Inspection
Facility views and infrastructure domains.
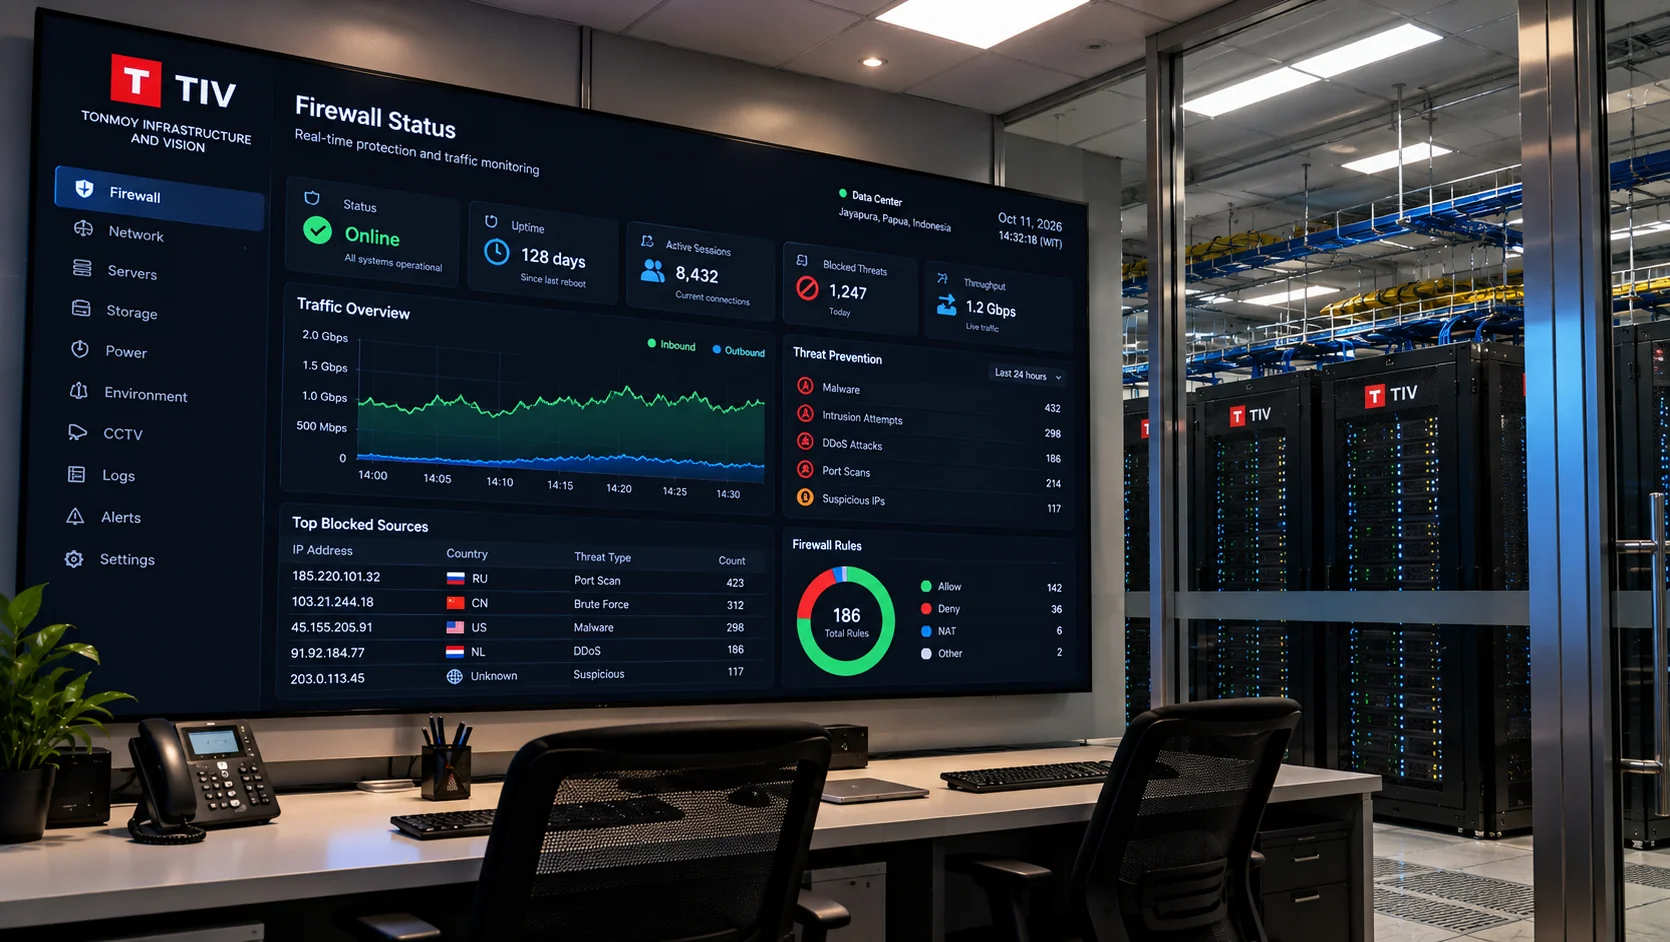
Explore the external environment, server white space, perimeter monitoring, and physical maintenance disciplines represented in TIV data center operations.
Exterior view
Exterior view
The data center
Exterior visualization of the TIV data center in Jayapura, Papua, Indonesia.
Shows the facility external environment, perimeter envelope, and physical infrastructure situated in Jayapura, Papua, Indonesia. Demonstrates regional deployment context, structural perimeter boundaries, and dedicated sovereign digital hosting.
Technical Principles
Location: Jayapura, Papua, Indonesia (Pusat Bisnis Jayapura)
Perimeter: Physical security boundaries and controlled building ingress
Deployment: Regional sovereign digital facility for internal TIV workloads
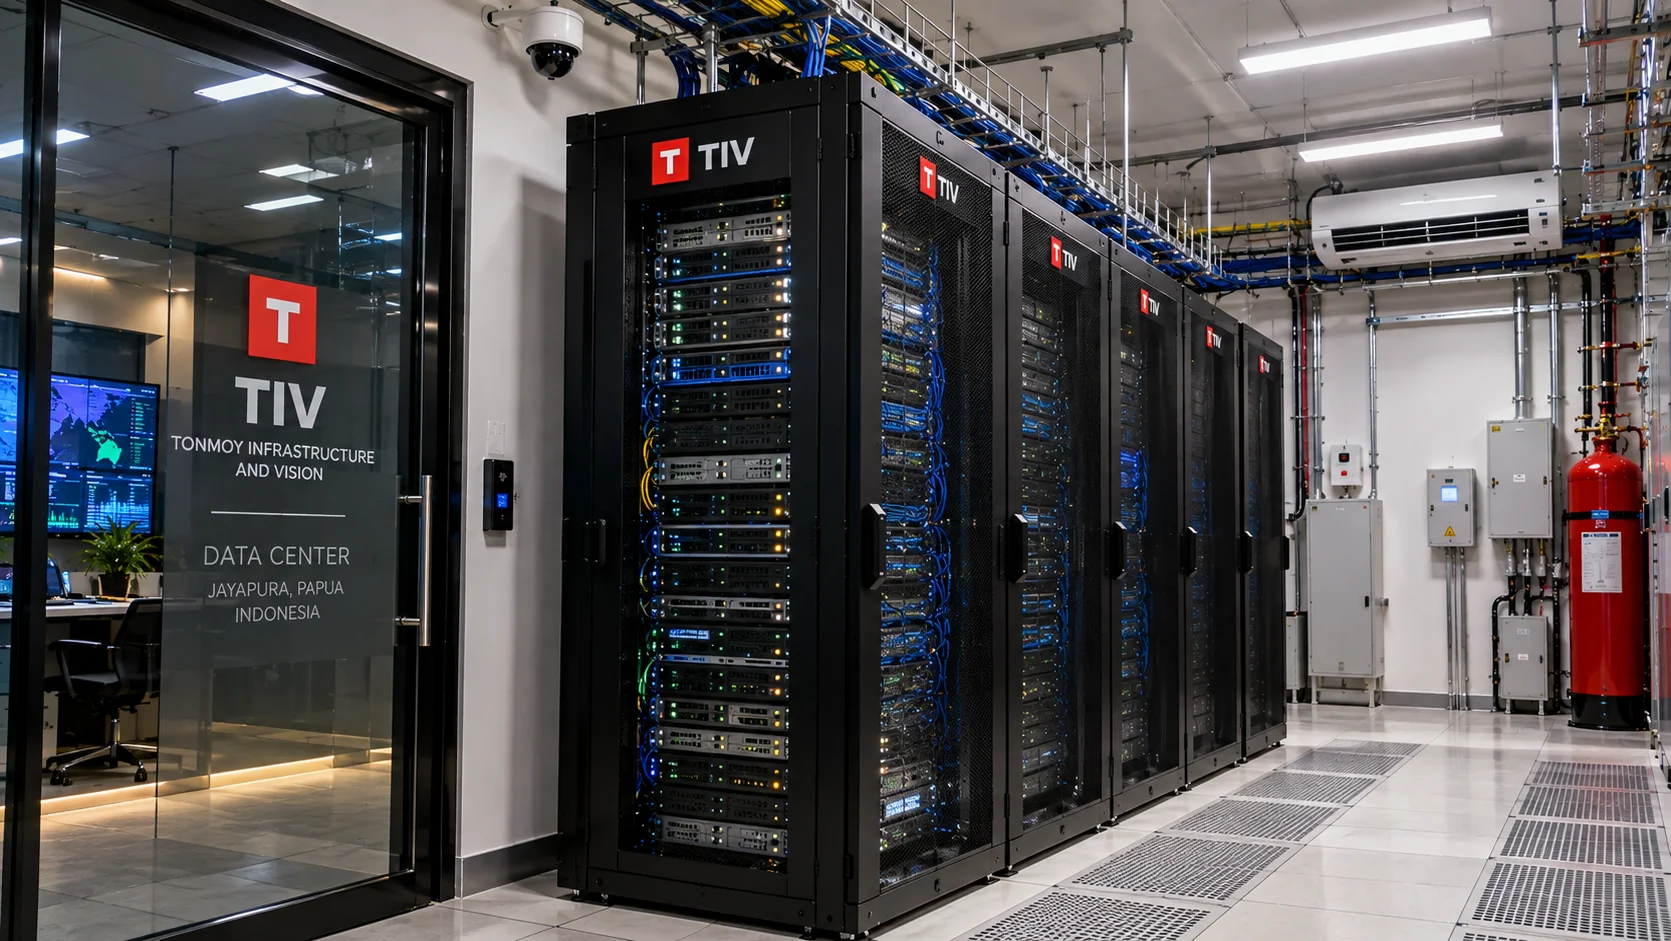
Server room
Server room
Computing infrastructure
View of server racks, network cabling, and supporting data center equipment.
Shows server racks, network equipment, structured cabling, and equipment-room organization without asserting that every visible piece of equipment exists at the physical site. Highlights high-density compute nodes hosting TIV platforms including OpenMail, Mercura, M31A, and Octate.
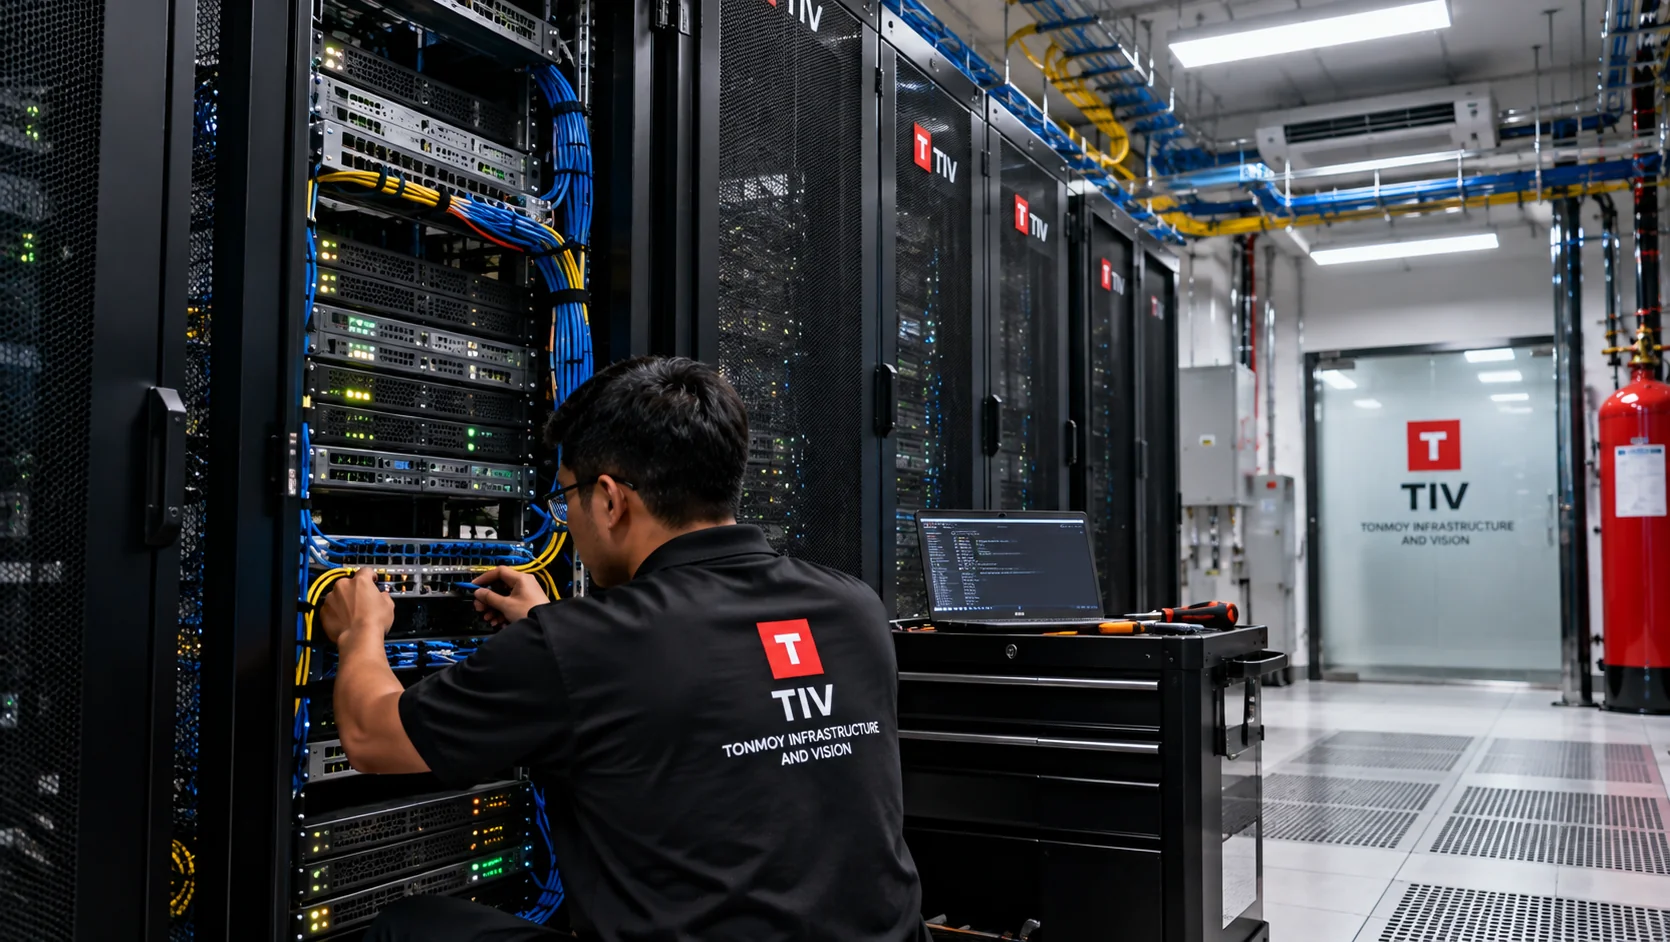
Notice: The technician depicted is a generated visualization demonstrating maintenance protocols and is not an actual TIV employee.
SCHEMATICTopology
Facility architecture and physical subsystem topology.
Schematic distribution path tracing dual utility feeds, auxiliary power generation, online UPS battery conditioning, modular server racks, and carrier meet-me demarcation.
FACILITY ARCHITECTURE
Sovereign Data Center Facility Topology
Dual Power Feeds · Jayapura Facility · Modular Racks
Power: Dual Independent Distribution Paths (A/B Feeds & Auxiliary Generator)Security: Aligned with ISO 27001 & SOC 2 Security PrinciplesLocation: Jayapura Sovereign Data Center Facility (Papua, Indonesia)
DOMAINSEngineering Areas
Six core infrastructure subsystems.
A structured overview of the facility computing, cabling, security, power distribution, climate management, and physical access controls.
01
Computing and server infrastructure
White-space compute nodes hosting TIV core software platforms (OpenMail, Mercura, M31A, Octate), authoritative DNS daemons, and internal build services.
Engineering Principles
Modular equipment rack deployment designed for scalable compute and storage expansion
Linux cgroups v2 resource ceilings (cpu.max, memory.max) and POSIX rlimits process confinement
ZFS and NVMe storage pools for durable repository mirrors and cryptographic state records
Out-of-band serial and IPMI hardware monitoring interfaces
Operational Considerations
Proactive processor temperature profiling and ECC memory error logging
Cold-restart runbooks and reproducible system image configurations
Thermal intake monitoring to prevent component hotspots
Confirmed ScopeHost environment for TIV software platforms and sovereign services in Jayapura, Papua, Indonesia.
02
Network connectivity and cabling
High-throughput data transport linking computing clusters, local aggregation switches, and regional carrier interconnects.
Engineering Principles
Structured Cat6A and multimode/singlemode fiber patch cabling with strict bend-radius management
Top-of-Rack (ToR) switching architecture minimizing intra-rack cross-talk and latency
Color-coded patch discipline separating management, storage, and public transit paths
Carrier fiber demarcation into regional Indonesian telecommunications backbones
Operational Considerations
Scheduled optical budget and attenuation inspections
Automated link flapping alerts and interface error tracking
Dual upstream routing paths to prevent single points of network failure
Confirmed ScopeCarrier fiber demarcation supporting TIV authoritative DNS and mail routing.
Multi-factor physical authentication at facility perimeter and server room access points
Continuous electronic access logging and visitor escort requirements
Structured cleanroom discipline and dust containment protocols during hardware servicing
Cryptographic custody and tamper-evident tracking for hardware transit and component replacements
Operational Considerations
Scheduled preventive maintenance windows for fan cleaning, optical transceiver checks, and cabling hygiene
Mandatory documentation of all physical rack openings and hardware changes
Personnel depictions represent maintenance concepts and do not depict actual TIV staff members
Confirmed ScopeControlled physical access and sovereign facility maintenance in Jayapura, Papua, Indonesia.
RELIABILITYOperational Principles
Disciplined engineering over synthetic metrics.
How proactive observability, preventative maintenance, climate equilibrium, and deterministic isolation preserve operational integrity.
Proactive observability & telemetry
Continuous instrumentation across CPU junction temperatures, fan speeds, ECC memory parity errors, and optical link attenuation enables early anomaly detection before faults cascade into downtime.
Scheduled preventative runbooks
Strict operational runbooks govern optical patch inspections, battery internal resistance impedance testing, air filter replacements, and auxiliary generator test cycles under simulated load.
Equatorial climate equilibrium
Jayapura equatorial coastal climate demands continuous dew-point and relative humidity management. Hot/cold aisle isolation prevents hot air recirculation and thermal degradation.
Defense in depth & policy gates
Physical security boundaries, network perimeter packet filtering, and runtime confinement work in unison. Workloads like M31A enforce 11-stage policy gates and ASVS L1 hardening.
Cryptographic backup & recovery
ZFS snapshots, encrypted off-site cold storage mirrors, and reproducible declarative system configurations ensure deterministic cold-restart capabilities without unverified claims of instant recovery.
Honest reliability reporting
TIV deliberately avoids publishing unsubstantiated availability figures (e.g. 99.999% SLAs) without multi-year audited operational evidence. Reliability is earned through verifiable architecture and transparent accounting.
COORDINATESPhysical Location
Verified facility location in Jayapura.
The facility is established in Jayapura, Papua, Indonesia, positioning sovereign compute directly within Eastern Indonesia.
Organizations requiring dedicated bare-metal nodes, private cross-connects, or sovereign data isolation in Eastern Indonesia may initiate confidential technical consultations.